Cybersecurity & Compliance Services | HIPAA Ready
Home/Services/Cybersecurity
securitySecurity

Security from the first commit.

Cybersecurity and compliance services

Late security costs more. Set up before the first feature.

Request a security reviewarrow_forward
Frameworks we work against
HIPAASafeguards for health data
SOC 2Access, change and logging evidence
GDPRPrivacy rules, applied in practice
OWASPChecked against the most exploited risks
Zero trustEach person and service verified per request
01 · The problem

Unknown exposure.

A questionnaire can delay a deal. A breach costs more.

$4.99M

Global average cost of a data breach.

Source: IBM, 2026 Cost of a Data Breach Report
Common situations
Known vulnerabilities sit unpatched for months.
Passwords still live in config files.
Sensitive data is held without a written protection plan.
Nobody would notice a breach until a customer did.
Logs are collected but not reviewed.
02 · The basics

What is application security?

Practices that protect software and data from unauthorised access, from design through production. Includes access control, encryption, testing and compliance.

When done poorly
warning01

A breach typically costs more than prevention.

trending_down02

Failed security reviews delay sales.

report03

Gaps found late are expensive to fix.

03 · Related work

Built and in use.

Live systems delivered with our clients.
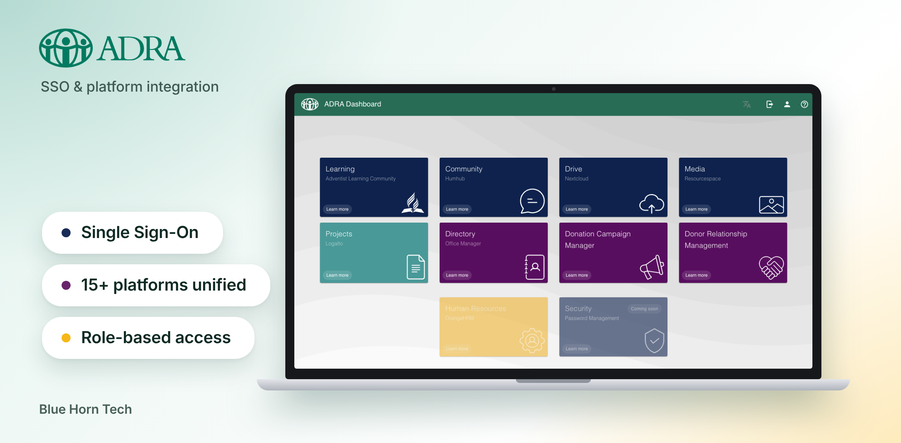
ADRA dashboard: single sign-on to every platform
Nonprofit · Identity

ADRA

Fifteen platforms, one login, a hundred countries.

Read case study
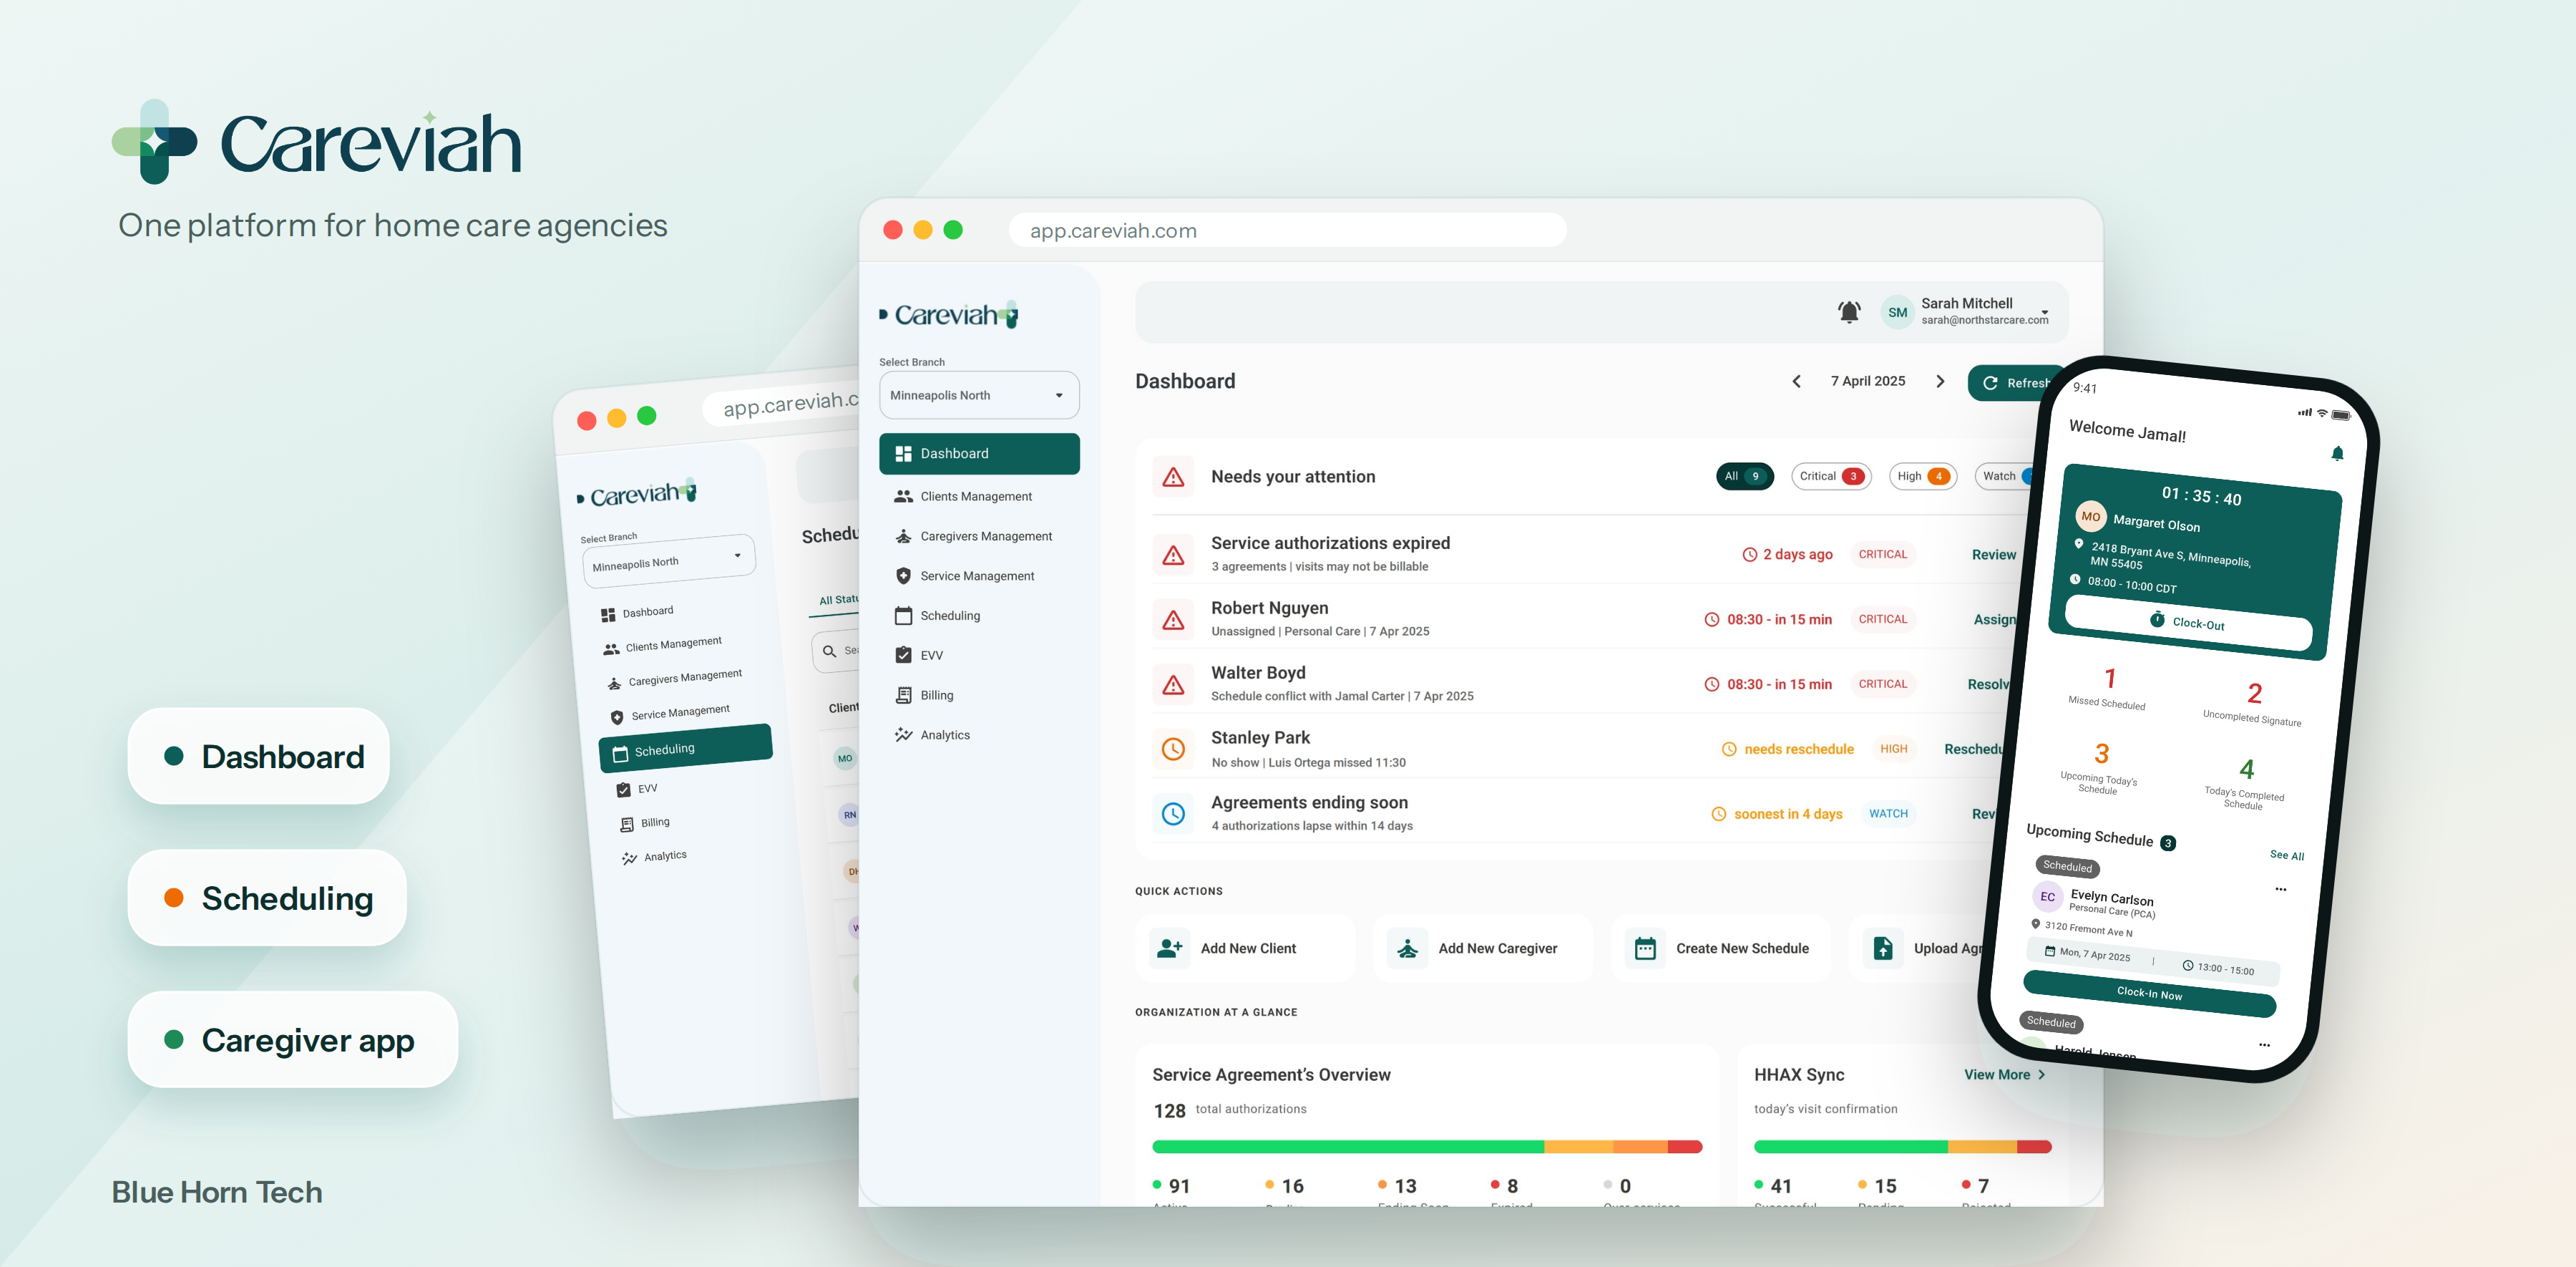
Careviah: one platform for home care agencies
Home care · Product

Careviah

Home care visits verified at the door. Scheduling, billing and reporting use that record.

Read case study
04 · The solution

Assess. Fix. Document.

policy

Security audit

Attacker’s view. Risks ranked.

schema

Threat modelling

Designed in. Cheaper than later fixes.

shield_moon

Hardening

Secrets out of code. Encryption. Least-privilege access.

assignment_turned_in

Compliance readiness

Controls and evidence for audit.

monitor_heart

Logging and monitoring

Logs of who did what. Alerts for real events.

groups

Team enablement

Incident runbooks.

05 · The process

How we work with you.

Step 01

Discover

We review your processes and identify priorities.

Step 02

Plan

Scope, timeline and price, agreed in writing.

Step 03

Deliver

Two-week cycles. Progress reviewed with you each cycle.

Step 04

Hand over

Staff trained, docs written, all assets in your account.

FAQ

Common questions.

What is included in a security assessment?

Attacker-view testing. Largest gaps fixed first.

Can you help with HIPAA compliance?

Yes. We have built HIPAA-ready systems.

How fast can we answer a security questionnaire?

Usually in an afternoon, once the evidence exists.

5 review slots this quarter

A security review in two weeks.

Send us a security questionnaire.

Book a 30-minute callarrow_forward